Architecting Secure Cloud Subnets and VPC Networks for Web Platforms
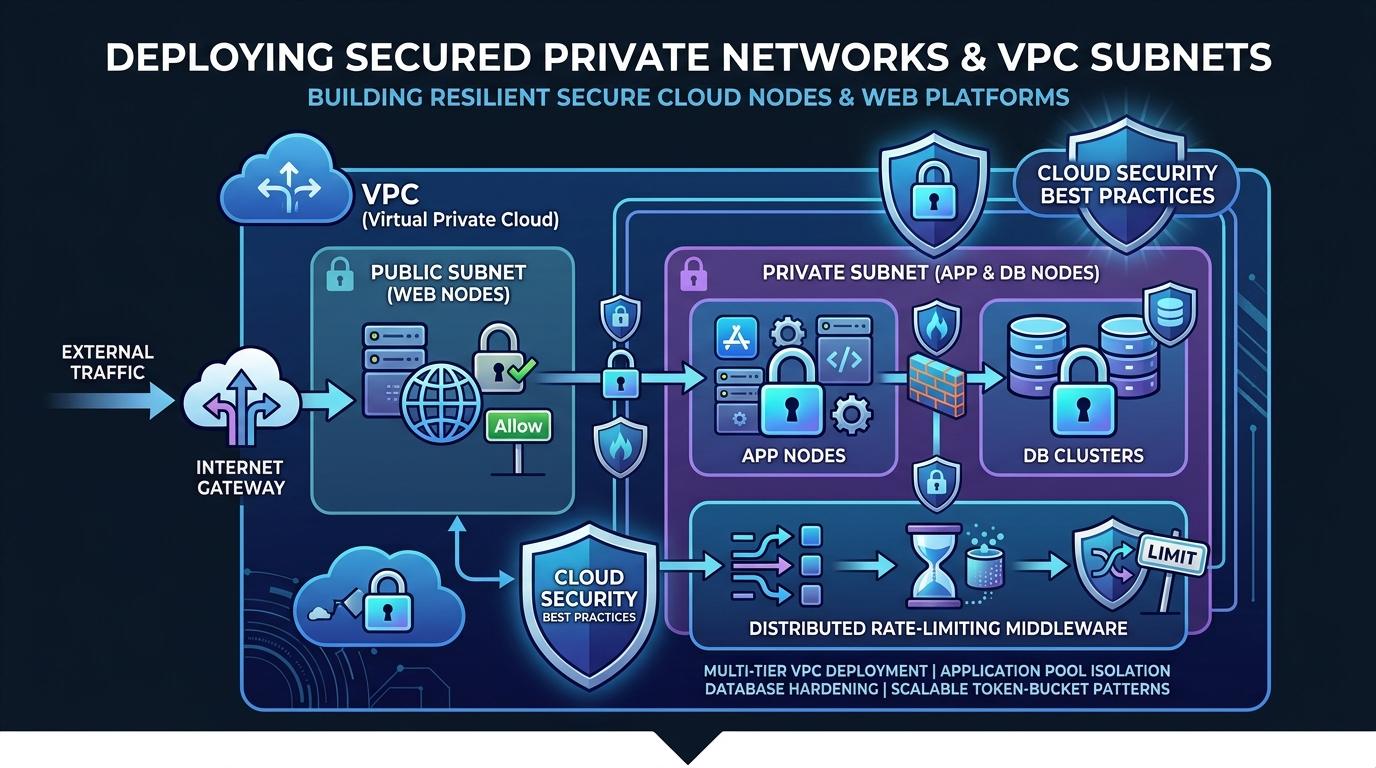
Learn cloud security best practices by deploying multi-tier Virtual Private Clouds (VPC), isolating application pools, and hardening database clusters.
Cloud Networking
Hardening Network Topologies: Isolating Production Environments using Private Subnets
Cloud Engineering • 12 Min Read
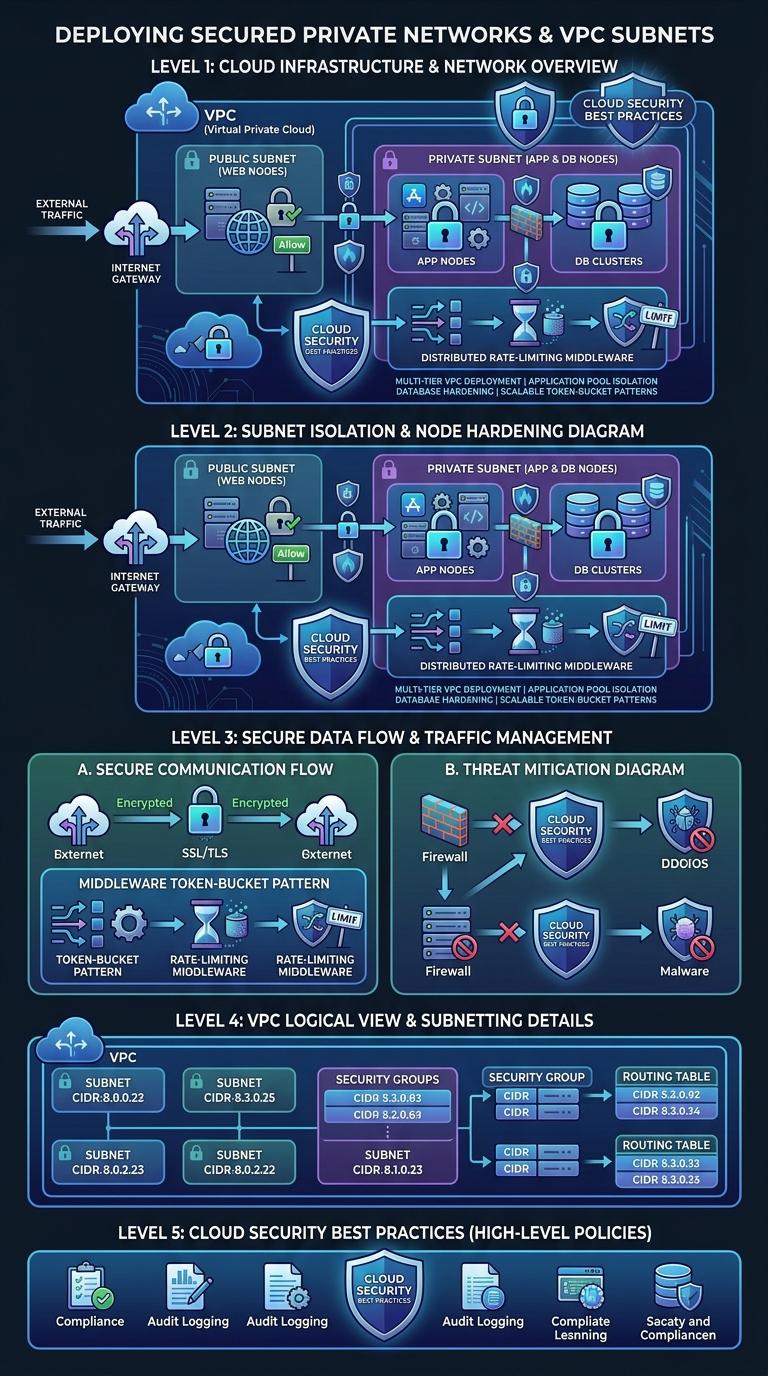
Why Direct Public Internet Mappings present Danger
Deploying application databases or cache servers with direct public-facing IP addresses exposes vital infrastructure components to brute-force network scans. Best practice relies on restricting public entry points exclusively to edge load-balancers, while shielding backend application instances within **isolated Virtual Private Cloud (VPC) subnets**. This strategy blocks direct outside attacks, requiring all external traffic to validate through your access control points first.
Declaring Secure Infrastructure Blocks via Declarative Configuration
Use infrastructure-as-code configuration tools to cleanly define your isolated subnet blocks and keep your public web gateways split from private resource links.
Terraform Network Mapping Target Layout
# Provision a hardened private subnet to house non-public system components
resource "aws_subnet" "isolated_backend_subnet" {
  vpc_id            = aws_vpc.primary_network_hub.id
  cidr_block        = "10.0.2.0/24" # Isolated space with no external internet route routes
  map_public_ip_on_launch = false

  tags = {
    Name = "Enterprise Isolated Tier"
  }
}
Infrastructure Golden Rule
To handle package updates safely from within isolated private subnets, install a secure NAT Gateway. This lets backend servers fetch code updates from the internet while continuing to block all unrequested inbound connections.
Leave a comment
Your email address will not be published. Required fields are marked *